Interview questions in CI/CD & Automation, page 2
How would you design a multi-arch build process and anticipate challenges?
Mention buildx or cross-compilation, split native and emulated builds, cache per-arch layers.
How would you integrate artifact signing into CI/CD and secure the keys?
Tests supply chain architecture and secrets management. A strong answer: remote HSM or KMS signing isolated from build runners, signature verification at deploy gates, and key rotation with audit logging.
What is a CI/CD quality gate? Give a simple example.
Thresholds blocking merges; a minimal new-code gate with 0 critical issues & 70% new-code coverage.
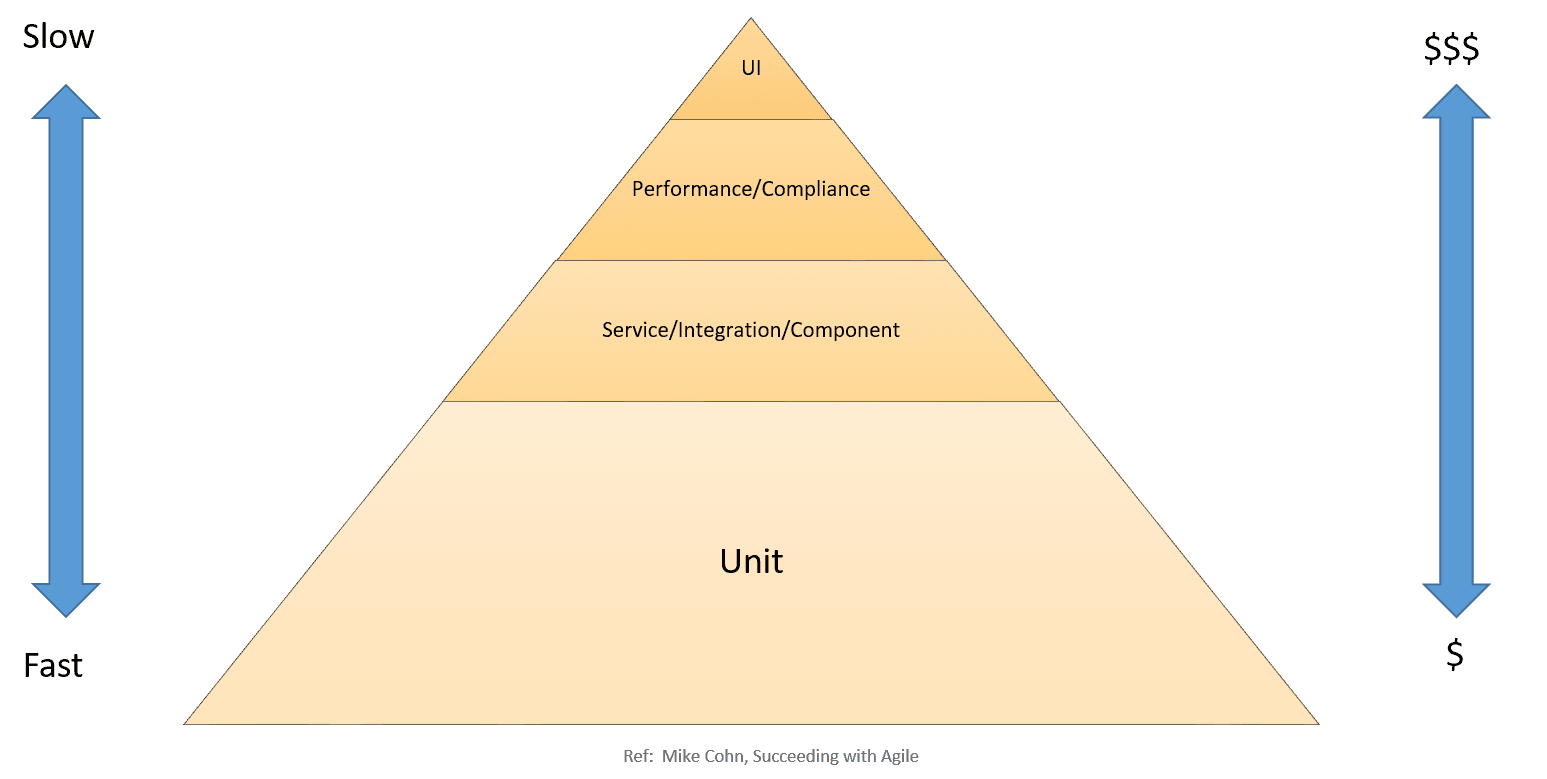
Difference between unit and integration tests and CI pipeline placement
Unit tests isolate code and run fast in the build stage; integration tests verify real wiring later. Target 70 percent unit tests.
How would you block merges when PR coverage drops 2%?
Upload coverage to Codecov, set a project status threshold of 2, and require the check in branch protection.
How would you integrate SAST into CI without alert fatigue?
This tests embedding security into workflow without killing velocity. Run SAST per commit, suppress false positives via rulesets, gate on high-severity findings first and block merges only after calibration. A red flag is zero-tolerance blocking on day one.
Smoke test fails after canary deployment. Design the automated rollback.
Tests self-healing pipeline design: freeze canary traffic, auto-redeploy the last good release, verify rollback health, and keep failed pods for forensics. Red flag: requiring manual approval or in-place fixes instead of an atomic rollout swap.
How would you diagnose, report, and mitigate E2E flakiness at scale?
Tests metric-driven pipeline hygiene versus retry band-aids. Strong answers baseline flakiness rates, identify offenders via CI history, quarantine chronic flakes from presubmit, and fix root causes like concurrency.
SNAPSHOT and RELEASE versions: differences and appropriate use
SNAPSHOTs are mutable; RELEASEs are immutable and tagged. Use SNAPSHOTs on feature branches and RELEASEs for main.
How do you version Docker images: Git SHA or SemVer?
Your grasp of immutable artifacts and traceability versus human-readable releases. Tag every build with Git SHA for immutability, then apply SemVer aliases only on promoted images. Treating floating tags like latest or v1 as safe production targets.
Explain proxy repositories in artifact managers and the problems they solve
Tests caching and supply-chain resilience in builds. Strong answers cover: local caching of upstream artifacts, shielding CI from external outages, and policy enforcement at the edge.
Promote an artifact from staging to release without rebuilding it
Tests immutable artifact discipline. Answer: promote by copying the binary or retagging the image digest, never recompiling, because rebuilds introduce dependency drift and untested bits.

Integrate artifact signing and vulnerability scanning into CI/CD
Build SBOMs, sign with ephemeral keys, scan registries, and enforce policy before deploy.
How can artifact management and CI identify affected services and block deployments?
Tests supply chain forensics and CI gating. Strong answers hit: SBOMs mapping transitive blast radius; artifact metadata tracing deployed versions; scan gates and quarantine policies blocking promotion.
How do you manage multi-arch container images under a single tag?
This tests image distribution and registry semantics. A strong answer covers manifest lists pointing to per-arch digests, Buildx as the builder driver, and the registry serving correct layer blobs.
What is Pipeline as Code and its benefits over GUI configuration?
Tests whether you treat delivery pipelines as versioned code. Strong answers define PaC as pipeline definitions in source control, citing branch automation, peer review, audit trails, and single source of truth.
Declarative vs scripted pipeline syntax: when to choose each?
This tests Jenkins Pipeline trade-off judgment. Contrast Declarative's opinionated blocks and guardrails with Scripted's raw Groovy flexibility; prefer Declarative for new projects unless complex flow control is needed.
How should you manage sensitive data in a committed pipeline file?
Tests that committed pipeline YAML must never store secrets. Answer: fetch at runtime via native secrets manager integrations; if needed, use masked, hidden, protected CI/CD variables; use typed CI/CD inputs for parameters.
How would you reuse pipeline steps across projects using PaC principles?
Tests DRY abstractions and coupling in CI/CD. Good answer: versioned reusable templates or libraries with parameterized inputs, consumed by composition. Red flag: raw copy-paste or one global pipeline forcing lockstep deployments.
How would you implement conditional logic in a pipeline?
Use if conditions with contexts like github.ref, separate trigger filters from runtime conditions, and add env rules.
We are hiring for this. Every open role lists the topics its interview covers, so you can prepare for the real thing rather than guessing.
See open roles