Interview questions in CI/CD & Automation, page 4
Prevent developer access to production secrets while preserving debuggability
Use dynamic short-lived credentials, break-glass with dual-control audit, and structured telemetry or synthetic transactions for debugging.
How do you securely manage and inject Helm secrets in CI/CD?
Tests secret lifecycle trade-offs in GitOps. Strong answers compare SOPS-encrypted values in Git, direct Vault injection for dynamic secrets, and External Secrets Operator to decouple secrets from charts.
Walk me through a production-ready Dockerfile for a web app
Tests multi-stage builds, layer caching, and security hardening. A strong answer covers a pinned slim FROM, multi-stage separation of build and runtime, ordered COPY for cache, and a non-root USER.

What is the difference between a Service and an Ingress?
This tests L4 versus L7 networking abstractions. A good answer says Services load-balance to Pods internally while Ingresses route external HTTP to Services via a controller, then gives a path-based scenario.
What are liveness and readiness probes, and what happens when each fails?
This tests whether you know the distinct kubelet actions for each probe failure. A strong answer: liveness failure restarts the container; readiness failure removes the Pod from Service endpoints and stops traffic.
Describe the difference between a Deployment and a StatefulSet
Tests stateful pod identity versus stateless scaling. Outline: contrast Deployments' interchangeable replicas with StatefulSets' stable hostnames, per-pod PVCs, and ordered rollout; give a database example.
How ensure Kubernetes pulls correct new image and why avoid :latest?
Tests immutable tagging and Kubernetes image pull behavior. Strong answers demand unique tags like git SHA, explicit deployment spec updates, and explain :latest's reproducibility failures across nodes.
Explain the concept of a sidecar container in Kubernetes
Tests Pod multi-container patterns. A strong answer defines sidecars as co-located helpers sharing network and storage, cites service mesh or log forwarding, and argues for reuse and separate lifecycles. Red flag: calling it another Pod or legacy workaround.
Compare Kubernetes Secrets versus environment variables for Pod credentials
Tests Kubernetes credential threat model across etcd and Git. Plain env vars leak into manifests and process lists; Secrets enable RBAC but are base64 by default and visible to nodes and authorized readers. Red flag: claiming Secrets are encrypted by default.
How do you diagnose and fix a Kubernetes OOMKilled application?
Tests cgroup enforcement versus scheduling. A strong answer verifies OOMKilled, compares limits to usage, then rightsizes requests to baseline and limits with headroom. Red flag: confusing requests with caps or blindly raising limits.
Design a zero-downtime Kubernetes Deployment strategy for a stateless microservice
Set RollingUpdate with maxSurge 1 and maxUnavailable 0; use readiness probes to gate traffic; set terminationGracePeriodSeconds and preStop to drain requests.

Rolling vs blue/green deployments: differences and trade-offs
Tests risk-cost-downtime judgment. Contrast rolling's gradual swap with blue/green's parallel swap; rolling is cheaper but mixes versions, while blue/green doubles capacity for instant rollback. Red flag: saying blue/green cheaper or rolling double-capacity
Explain canary releases and why choose them over rolling updates
This tests risk mitigation via user routing versus in-place replacement. A strong answer defines canary as exposing a subset to the new version first, contrasts rolling updates lacking user segmentation, and cites fast rollback.

What problem can a breaking API change cause during a rolling update?
Tests if you know rolling updates run mixed versions, so breaking API changes crash cross-traffic. Good answer: note old and new pods serve together, watch probes fail, and monitor 5xx spikes. Red flag: claiming Kubernetes isolates versions during rollout.
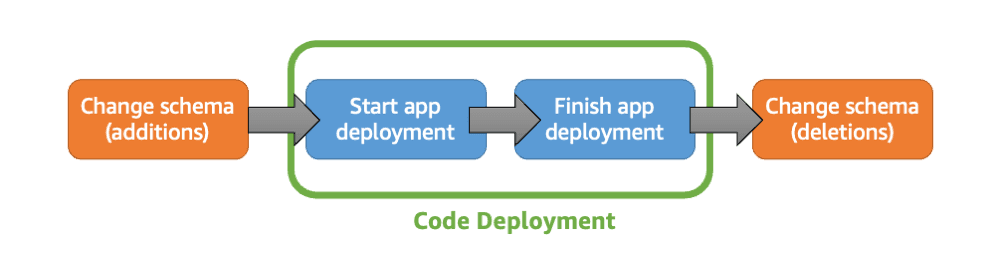
What are the major challenges of blue/green deployments with relational databases?
Tests decoupling schema and code changes in stateful blue/green deployments. Strong answers cover the additive-then-deletive pattern, backward compatibility for both app versions, and shared DB risks. Red flag: split DBs with no rollback or sync plan.
How would you automate canary deployment and what metrics decide rollback?
This tests progressive delivery maturity. Strong answers cover traffic splitting (10% to 100%), automated 5-10 minute health gates, and rollback triggers like error rate and p99 latency.
How can a service mesh facilitate canary or A/B testing?
Tests mesh-level traffic control decoupled from app releases. Strong answers name traffic shifting, request routing, ingress gateways, and telemetry-driven rollback. Red flag: citing mTLS alone and omitting observability automation.

Canary vs shadow deployments: use cases and requirements
This tests whether you distinguish user-facing rollouts from invisible duplication. Canary routes some real users to new code to limit blast radius; shadow mirrors traffic to an isolated clone to test performance without user impact.
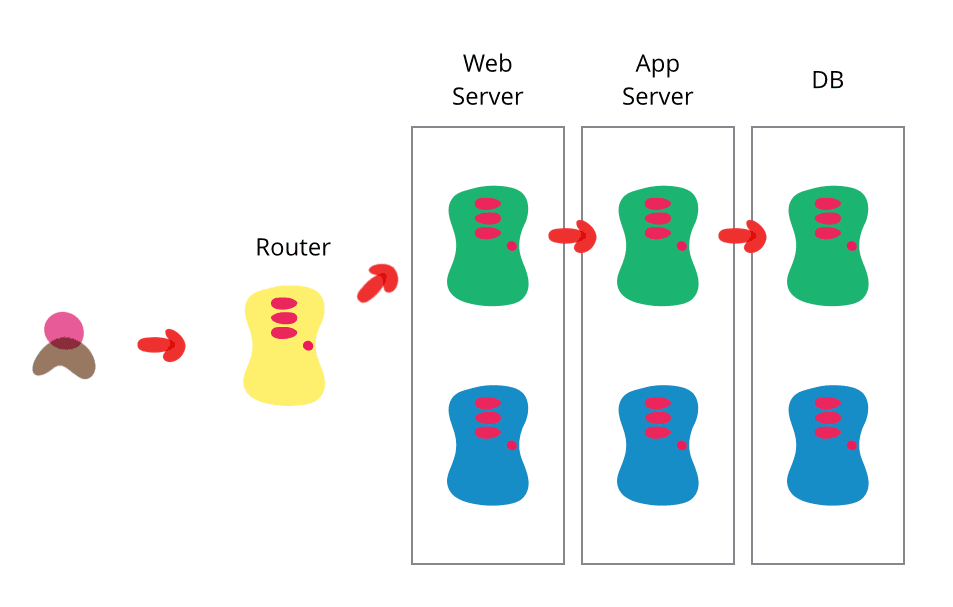
Blue/green deployment fails during switch-over with partial decommissioning; recovery and process changes?
Tests whether you can recover when a blue/green rollback path is compromised. Strong answers stop the bleed, revive blue if possible, and mandate keeping blue fully warm until green is stable. Red flag: "just roll back" ignoring partial decommissioning.

How do you deploy a hotfix during a multi-stage canary release?
Dark-launch the fix to the canary cohort, preserve metrics, then jointly promote.
We are hiring for this. Every open role lists the topics its interview covers, so you can prepare for the real thing rather than guessing.
See open roles