Interview questions in CI/CD & Automation, page 7
How do you implement security policies as code across CI pipelines?
This tests operationalizing Policy as Code for security scanners at scale. Strong answers cover centralized version-controlled rules consumed by CI pipelines with automated gates and exception workflows. Red flag: teams maintaining independent scanner configs.
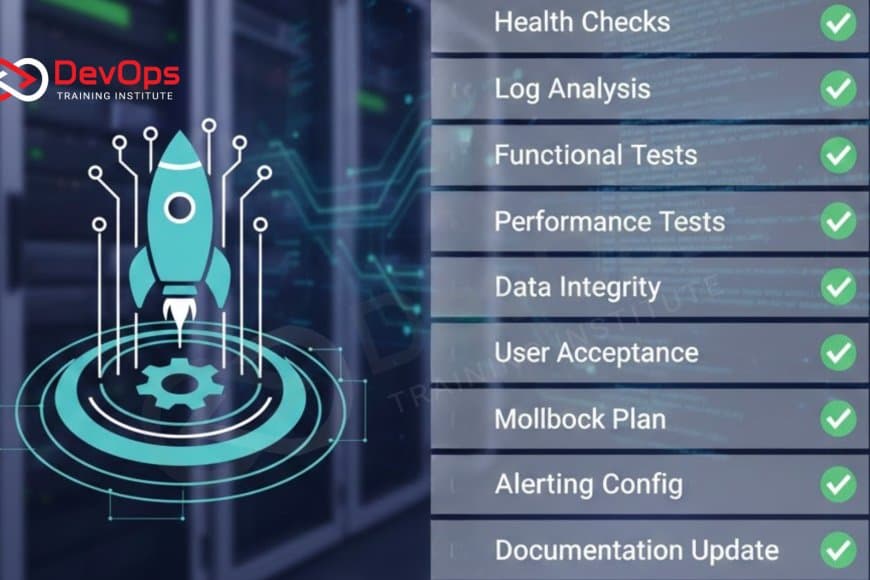
How do you add a basic post-deployment health check in CI/CD?
Tests deployment validation beyond exit-code success. Outline: add a post-deploy stage that probes an HTTP endpoint, checks status code and latency, validates critical dependencies, and triggers rollback on failure.
Explain .gitignore and its impact on faster, reliable, secure CI builds
Exclude build artifacts to shrink clones and stabilize cache keys; block secrets from runners.
What is Git LFS and what are its CI/CD trade-offs?
This tests whether you understand Git's object model limits. A strong answer covers pointer indirection, smudge filters, and the shift of download burden to the LFS server in CI. A red flag is claiming LFS eliminates large file transfers entirely.
What is static analysis in automated builds, with examples?
This tests if you treat static analysis as a pre-runtime quality gate. A strong answer says it shifts feedback left via non-execution scans, citing cyclomatic complexity or unhandled promise rejections.
What is a build artifact? Give Java, JS, and C++ examples.
Define artifacts as compiled outputs; list JAR/WAR for Java, webpack bundle for JS, and binary/.so for C++; note immutability.
Design a selective build strategy for a large monorepo
Tests monorepo dependency graph reasoning. Good answers model a DAG, compute reverse deps of the changed library, rebuild only affected targets via Bazel or Nx, and cache remotely. Red flag: directory triggers, full rebuilds, or testing the library alone.
What is an artifact repository and why not just a shared filesystem?
Tests your grasp of immutability, metadata, and access control for build artifacts. A strong answer covers versioning, checksums, RBAC, and API retrieval that NFS lacks. Red flag: saying a shared filesystem is simpler and therefore enough for production.
How would you create and distribute reusable IaC components at scale?
This tests platform engineering governance at scale. A strong answer proposes a versioned module registry, policy-as-code guardrails, automated validation pipelines, and self-service documentation.
Design short-lived dynamic database credentials and their security benefits
This tests automated least-privilege credential lifecycle design. A strong answer covers a secrets broker with database plugins, short TTL leases tied to workload identity, and automatic revocation. Red flag: manual rotation or long-lived CI variables.
What strategies reduce DAST scan time while maintaining security coverage?
It tests balancing security depth with CI velocity through DAST tuning. A strong answer covers incremental scans, parallel workers, scoped targets, and shift-left complements.
Design a workflow for managing security scanner vulnerabilities
This tests scaling security without developer noise fatigue. A strong answer covers centralized ingestion, severity SLAs with exploitability, auto-triage rules, and CI gates on critical findings only. A red flag is forcing manual review of all scanner output.
Design a golden path CI/CD pipeline for a Go API
Propose build, test, SAST, containerize, deploy stages with hooks or config overlays for flexibility.
We are hiring for this. Every open role lists the topics its interview covers, so you can prepare for the real thing rather than guessing.
See open roles