Easy everything in DevOps & Cloud, page 6
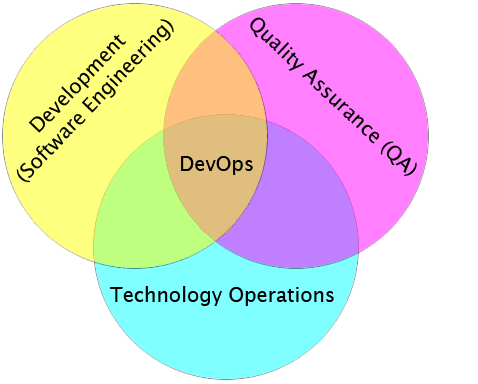
Explain GitOps and how an agent knows when to apply changes
Tests declarative infrastructure and pull-based reconciliation. A strong answer says Git is the source of truth and the agent polls or watches for drift, then applies diffs. Red flag: calling a push-based CI pipeline GitOps.
What is SAST and which CI/CD stage integrates it best?
Define SAST as source-code scanning; run it in the test stage on every commit; note early detection is cheapest.

What is the difference between a Service and an Ingress?
This tests L4 versus L7 networking abstractions. A good answer says Services load-balance to Pods internally while Ingresses route external HTTP to Services via a controller, then gives a path-based scenario.

What is IaC and its CI/CD benefits over manual provisioning?
Cover descriptive models, idempotency, and on-demand environments for repeatable CI/CD.
How do Docker images and containers differ and relate?
This tests your grasp of the immutable template versus mutable runtime boundary. A good answer: an image is a read-only layered template with code and dependencies; a container is a runnable instance with a writable layer on top.
ConfigMap decouples config from container images
A ConfigMap is a key-value store that injects configuration into pods without rebuilding the image. Use it for feature flags, database hostnames, or any non-secret settings. Editing one does not restart existing pods, so stale config is the common footgun.
How does shared responsibility shift between IaaS and SaaS?
Tests your understanding of security ownership across cloud stacks. Strong answer: in IaaS you own OS, apps, and network controls; in SaaS you only own data, identities, endpoints, and accounts while the provider manages the rest.
Explain the difference between IaaS, PaaS, and SaaS with examples
This tests your grasp of cloud abstraction layers and shared responsibility. A strong answer maps IaaS to raw infrastructure like EC2, PaaS to managed runtimes like Heroku, and SaaS to end-user apps like Gmail.
AWS SDK: Code That Operates Your Cloud
The AWS SDK turns AWS API calls into native code so your app can command S3 or DynamoDB directly. It handles auth, retries, and formatting automatically. The footgun: forgetting region or credentials causes silent failures that look like network errors.
IAM: The Gatekeeper Framework
IAM is the framework that decides who gets through the door and what they can touch inside your systems. It governs every employee transition, from onboarding to departure. The trap is treating IAM as a one-time setup rather than an ongoing lifecycle process.
GitLab Flex merges seats and AI into one budget
GitLab Flex reshapes one annual budget monthly across seats, AI credits, and features without re-procurement. Engineering leaders can shift spend from idle seats to agent usage instead of guessing headcount six months out. Ask at renewal.
GitLab Orbit unifies code lifecycle in live graph
GitLab Orbit beta unifies code, pipelines, and ownership in a live graph. Compare the Market tests show Orbit-grounded reviewers hit 70% accuracy versus 58% for RAG.
GitLab patches 13 CVEs including SAML account takeover flaw
GitLab 19.0.2, 18.11.5, and 18.10.8 patch 13 security flaws, including four High-severity CVEs like SAML account takeover (CVSS 8.7) and unauthenticated API DoS. Self-managed instances must upgrade immediately; GitLab.com is already patched.

How do you manage secrets for hundreds of services in centralized CI/CD?
It tests secret sprawl prevention and least privilege in CI/CD. Answer: use a secrets manager with RBAC, short-lived credentials, runtime injection, and audit logs. Red flag: secrets in Git, plain env vars, or one shared master key.
How do you version shared CI steps and handle breaking changes?
This tests CI hygiene and consumer safety. Pin shared steps to immutable tags or SHAs, use semantic versioning, and force consumers to opt into breaking changes. Red flag: referencing a mutable branch like main for reusable workflows.
Describe high-level steps to onboard a microservice via self-service CI/CD
Tests platform thinking and developer experience design. A strong answer outlines a golden path: templated repo setup, standardized build/test stages, environment promotion, and observability hooks, plus guardrails not blockers.
Walk me through deploying a new version using a GitOps workflow
Merge updates manifests; the GitOps controller compares desired state in Git to live state and reconciles.
Blue/green vs canary release: differences and when to choose each.
This tests release-automation risk mitigation. A strong answer contrasts instant full-environment swaps with gradual traffic shifts, pairing blue/green with hotfixes and canary with risky changes. A red flag is calling them identical or ignoring blast radius.
What are the four Golden Signals for service health monitoring?
Tests whether you can name the four essential metrics—latency, traffic, errors, saturation—and explain why each matters for detecting user-facing regressions after a release, rather than drowning in infrastructure noise.
Committed an API key to Git. Describe two automated CI/CD prevention methods.
This tests layered secret protection in Git workflows. A strong answer names pre-commit scanning and server-side push protection or pipeline scanning. Mention rotating that key. A weak answer only suggests manual review without automated gates.
We are hiring for this. Every open role lists the topics its interview covers, so you can prepare for the real thing rather than guessing.
See open roles