Intermediate everything in Mobile Dev, page 33
Google Play's Target API Level Requirement
Think of targetSdkVersion as a contract with Android. You promise your app handles all new security and privacy features up to that OS version. Google Play enforces this, blocking updates that target old APIs to protect users.
In-app Updates: Update Your App Without Leaving It
In-app updates prompt users to update without leaving your app. Use the 'Flexible' flow for routine updates and the 'Immediate' flow for critical fixes. The footgun is overusing the disruptive 'Immediate' flow for non-critical changes.
Play Core Library: Your App's Runtime API to the Play Store
The Play Core Library is your app's direct line to the Google Play Store at runtime. Use it to request features like in-app updates, on-demand modules, or user reviews without leaving the app.
Staged Rollouts: Limit Your Update's Blast Radius
Staged rollouts are a safety net, letting you release an update to a small percentage of users first. This lets you find crashes or major bugs before they affect everyone. The footgun: halting a rollout only stops new users from getting the update, it doesn't.
Google Play Dynamic Delivery: Ship Features On-Demand
Shrink your app's initial install size by delivering features on-demand. Instead of one giant APK, Dynamic Delivery sends a small base app, then downloads larger features like AR modes or special tools only when the user needs them.
App Signing by Google Play: Trust Google with Your Keys
App Signing by Google Play separates your app's identity from the key you use for uploads. Google manages the final, user-facing signing key, which is mandatory for new apps. The footgun is thinking your upload key is the final key; losing it is recoverable.
Android Biometric Authentication: The BiometricPrompt API
Android's BiometricPrompt is a unified API for fingerprint, face, or iris scans, replacing older, fragmented methods. Use it to authorize payments or unlock features. The footgun: never assume a specific biometric type is available; always have a fallback.
EncryptedSharedPreferences: Secure Key-Value Storage on Android
EncryptedSharedPreferences is a drop-in replacement for SharedPreferences that automatically encrypts keys and values, protecting sensitive data at rest. Use it to store small, sensitive data like API tokens. The main footgun is mismanaging the master key.

Android Keystore System
The Android Keystore System stores cryptographic keys in hardware backed secure storage instead of app memory or disk. Apps can use the keys to sign or encrypt data, but the raw key material never leaves the secure environment, even on a rooted device.
Android App Startup: From Cold to Hot
App startup has three types: cold, warm, and hot. Optimization focuses on the cold start—when the app launches from scratch. This is critical for user retention, as slow launches are a common reason for uninstalls. The footgun: don't just test warm starts.
Espresso for Android UI Testing
Espresso is an Android framework for automated UI tests. As an instrumented test, it runs on a device or emulator to simulate user interactions, helping you verify app behavior and UI correctness as part of a complete testing strategy.
Robolectric: Run Android Unit Tests on the JVM
Robolectric runs Android unit tests on a regular JVM, not a slow emulator. Use it in CI/TDD to test logic like Activity lifecycles without the minutes-long build-deploy cycle. The footgun is over-mocking; Robolectric tests behavior, not just implementation.
ActivityScenario: Test Your Android Activities in Isolation
ActivityScenario lets you launch and control an Android Activity's lifecycle within an instrumented test. Use it to verify UI behavior during events like screen rotation or process death, isolating the component for reliable testing.
AndroidX Test: The Standard Android Testing Toolkit
AndroidX Test offers a unified API for all Android testing, from local unit tests to on-device UI automation. It's the standard for building robust, testable apps. The footgun: accidentally bundling test-only dependencies into your production APK.
AlarmManager: Scheduling Precise Future Tasks in Android
AlarmManager is Android's system-wide alarm clock for your app, letting you run code at a specific time, even if your app is closed. Use it for time-sensitive tasks like calendar notifications. The footgun: alarms are wiped on reboot and must be re-registered.
@HiltViewModel: Simplified ViewModel Injection
@HiltViewModel automates creating ViewModels with dependencies. Instead of writing custom factories, just annotate the ViewModel and its constructor. It's the standard for injecting dependencies like repositories into ViewModels in a Hilt-powered Android app.
Moshi: Modern JSON for Kotlin & Android
Moshi is a modern JSON library that maps JSON strings to your Kotlin/Java objects. It's a translator between API text and your app's data classes, built with Kotlin-first features. The footgun: Kotlin classes require Moshi's codegen or reflection adapter.

Handling API State with a Sealed Class Wrapper
Treat API calls as states, not just data. A sealed class wrapper (Success, Error, Loading) models these states for your UI. Use this with Retrofit to show spinners or errors without crashing. The footgun: don't scatter try-catch blocks; centralize them.
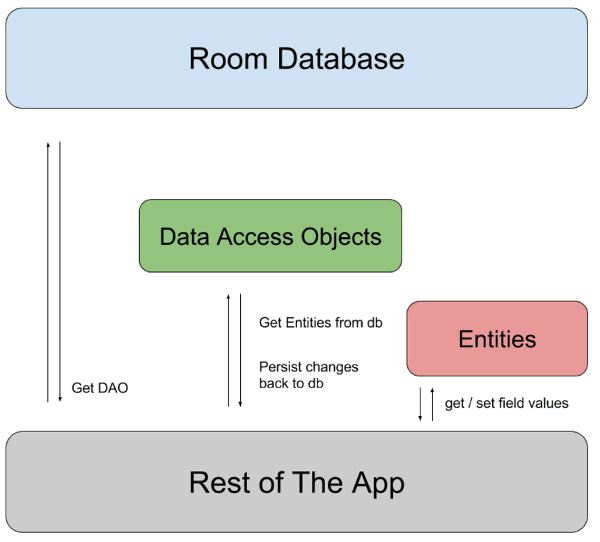
Scoped Storage: Your App's Private File Cabinet
Scoped Storage gives your app a private file cabinet on external storage, not a key to the whole building. It's the default on modern Android for saving data or accessing media. The footgun: don't use direct file paths to shared files; you must use new.
App-Specific Storage: Your App's Private Locker
Think of app-specific storage as a private locker for your app's data, automatically cleaned up on uninstall. Use it for cache, settings, or internal data. The footgun: assuming this data is permanent—it's deleted when the user uninstalls.
We are hiring for this. Every open role lists the topics its interview covers, so you can prepare for the real thing rather than guessing.
See open roles