Interview questions in CI/CD & Automation, page 5
What is SAST and which CI/CD stage integrates it best?
Define SAST as source-code scanning; run it in the test stage on every commit; note early detection is cheapest.
Committed an API key to Git. Describe two automated CI/CD prevention methods.
This tests layered secret protection in Git workflows. A strong answer names pre-commit scanning and server-side push protection or pipeline scanning. Mention rotating that key. A weak answer only suggests manual review without automated gates.
How do you investigate and resolve a critical transitive dependency vulnerability?
It tests transitive CVE triage. A strong answer reproduces the finding, traces the dependency path, upgrades the direct dependency if possible, and considers build-tool overrides otherwise. Red flag: ignoring it as transitive or blind upgrades without tests.

Compare SAST and DAST. Why use both, and their limits?
Tests whether you understand complementary security testing layers in CI/CD. A strong answer contrasts static source analysis without execution against dynamic runtime attack simulation and explains that relying on only one leaves applications vulnerable.
How would you integrate automated security scanning for Terraform in CI/CD?
Run Checkov or TFLint in CI to block builds; catch open security groups, missing encryption, secrets in code, and bad IAM.

How would you use a Kubernetes Admission Controller as CI/CD security gate?
Tests pre-deployment enforcement via admission webhooks. Strong answers: ValidatingAdmissionWebhooks blocking bad manifests, Pod Security Standards restricted profiles, and OPA/Gatekeeper for image signatures. Red flag: confusing with RBAC or runtime scanning.
What are the four Golden Signals for service health monitoring?
Tests whether you can name the four essential metrics—latency, traffic, errors, saturation—and explain why each matters for detecting user-facing regressions after a release, rather than drowning in infrastructure noise.
How do you diagnose a progressively slower CI pipeline?
Profile stage durations and critical path, audit runner CPU/memory/disk, flag flaky or late-failing tests.
Design an automated rollback process when deployment error rates spike
Gate on error-rate and latency thresholds; use blue-green deploys to limit blast radius; require human approval for stateful rollbacks.
How would you use distributed tracing to debug a deployment latency issue?
This tests causal request-path analysis beyond aggregate metrics. A strong answer filters traces by the new version, finds the exact regressed span, and compares it to a pre-deployment baseline.
How would you instrument CI/CD to measure a DORA metric accurately?
Tests mapping DORA definitions to pipeline events. A strong answer picks one metric, defines exact boundaries from merge to production, and correlates deployments with incidents.
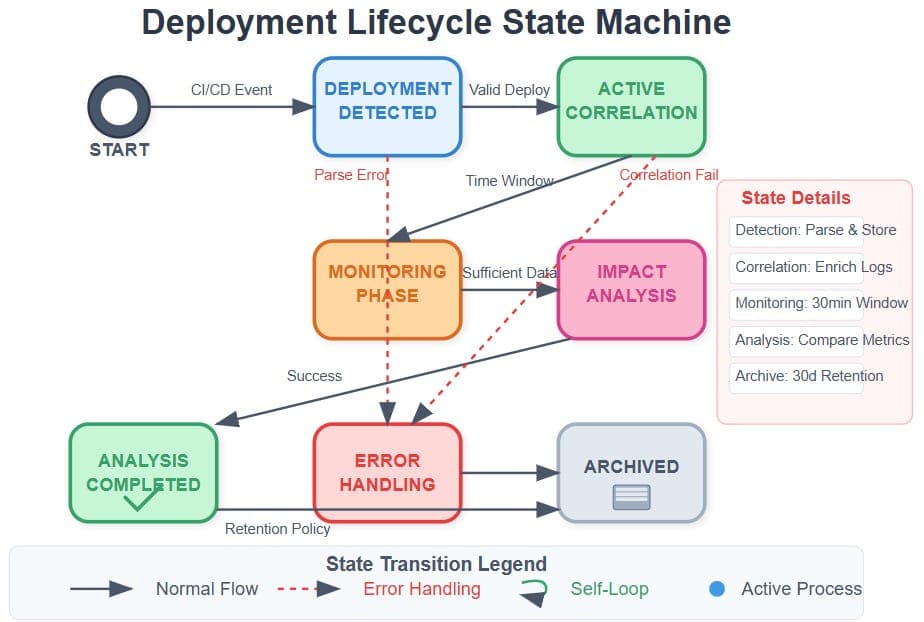
Design a system correlating CI/CD deployments with observability metrics
Tests event-driven correlation and temporal join patterns across distributed data. Strong answers outline: async deploy event ingestion, time-windowed metric joins with version tags, and handling clock skew.
What statistical methods automate canary-baseline comparison and handle noise?
Tests statistical rigor in automated canary analysis. Strong answers use non-parametric tests, multi-metric aggregation with effect-size gates, MAD-based outlier rejection, and smoothing windows.

How do you unify real-time CI/CD health across hundreds of microservices?
Canonical event schema over an event bus; domain-level SLI views; federated ownership with golden paths.
Explain GitOps and how an agent knows when to apply changes
Tests declarative infrastructure and pull-based reconciliation. A strong answer says Git is the source of truth and the agent polls or watches for drift, then applies diffs. Red flag: calling a push-based CI pipeline GitOps.
Blue/green vs canary release: differences and when to choose each.
This tests release-automation risk mitigation. A strong answer contrasts instant full-environment swaps with gradual traffic shifts, pairing blue/green with hotfixes and canary with risky changes. A red flag is calling them identical or ignoring blast radius.
Walk me through deploying a new version using a GitOps workflow
Merge updates manifests; the GitOps controller compares desired state in Git to live state and reconciles.
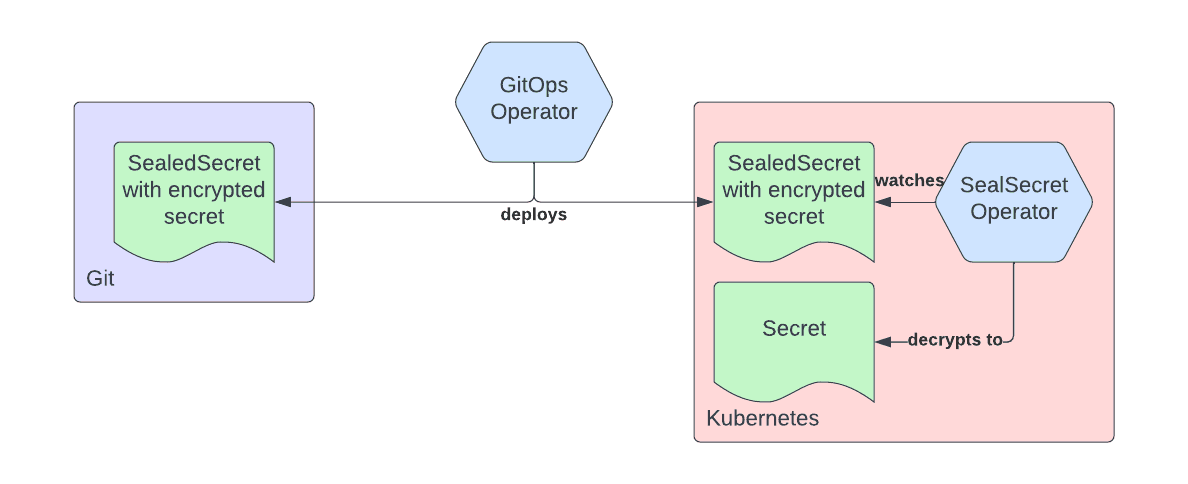
How do you secure secrets in a GitOps repository?
Tests whether you treat Git as source of truth while excluding plaintext credentials. A strong answer covers encrypting at rest with SOPS or Sealed Secrets, external stores like Vault, and operator workflows.
Two common GitOps repository layouts for multiple environments
Tests GitOps state-store trade-offs beyond single-cluster demos. Contrast a monorepo with directory overlays against repo-per-env; weigh polling overhead, blast radius, and promotion flow. Recommending branch-per-env destroys immutability and invites drift.
Automate a canary release with a 1% 5xx error threshold
This tests wiring an SLO into an automated canary loop. A strong answer covers traffic splitting via a mesh or ingress, an analysis query to Prometheus for 5xx rate, and auto-promote or abort logic.
We are hiring for this. Every open role lists the topics its interview covers, so you can prepare for the real thing rather than guessing.
See open roles