Advanced everything in CI/CD & Automation, page 2
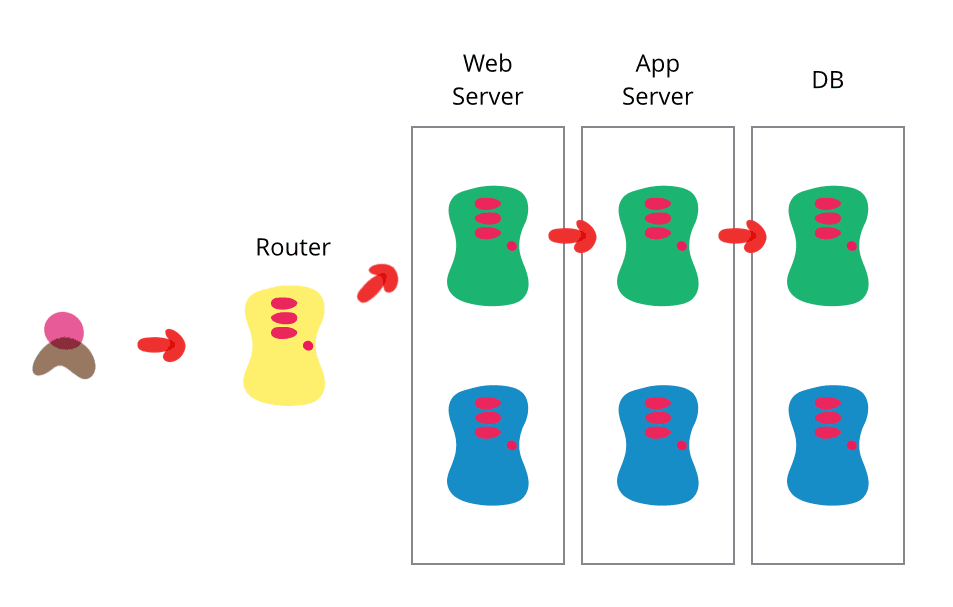
Blue/green deployment fails during switch-over with partial decommissioning; recovery and process changes?
Tests whether you can recover when a blue/green rollback path is compromised. Strong answers stop the bleed, revive blue if possible, and mandate keeping blue fully warm until green is stable. Red flag: "just roll back" ignoring partial decommissioning.

Canary vs shadow deployments: use cases and requirements
This tests whether you distinguish user-facing rollouts from invisible duplication. Canary routes some real users to new code to limit blast radius; shadow mirrors traffic to an isolated clone to test performance without user impact.

Design a zero-downtime Kubernetes Deployment strategy for a stateless microservice
Set RollingUpdate with maxSurge 1 and maxUnavailable 0; use readiness probes to gate traffic; set terminationGracePeriodSeconds and preStop to drain requests.
How do you diagnose and fix a Kubernetes OOMKilled application?
Tests cgroup enforcement versus scheduling. A strong answer verifies OOMKilled, compares limits to usage, then rightsizes requests to baseline and limits with headroom. Red flag: confusing requests with caps or blindly raising limits.
Compare Kubernetes Secrets versus environment variables for Pod credentials
Tests Kubernetes credential threat model across etcd and Git. Plain env vars leak into manifests and process lists; Secrets enable RBAC but are base64 by default and visible to nodes and authorized readers. Red flag: claiming Secrets are encrypted by default.
How do you securely manage and inject Helm secrets in CI/CD?
Tests secret lifecycle trade-offs in GitOps. Strong answers compare SOPS-encrypted values in Git, direct Vault injection for dynamic secrets, and External Secrets Operator to decouple secrets from charts.
Prevent developer access to production secrets while preserving debuggability
Use dynamic short-lived credentials, break-glass with dual-control audit, and structured telemetry or synthetic transactions for debugging.
Infrastructure apply fails midway. What is the state and your immediate steps?
This tests partial-state reasoning and safe recovery. A strong answer halts automation, inspects state for blast radius, then chooses idempotent roll-forward or rollback with canary validation.

Discuss security implications of developer-defined PaC pipelines
It tests balancing CI/CD flexibility with defense-in-depth against secret exfiltration. Cover scoped build identities, branch policies, approval gates, and sandboxed fork builds. Red flag: shared service connections or unrestricted pipeline admin rights.
Standardize and update CI/CD across hundreds of microservices without per-repo edits
Repos use a thin wrapper importing versioned shared-library templates; a control plane rolls out updates with canary validation.
How do you manage multi-arch container images under a single tag?
This tests image distribution and registry semantics. A strong answer covers manifest lists pointing to per-arch digests, Buildx as the builder driver, and the registry serving correct layer blobs.

Integrate artifact signing and vulnerability scanning into CI/CD
Build SBOMs, sign with ephemeral keys, scan registries, and enforce policy before deploy.
How would you diagnose, report, and mitigate E2E flakiness at scale?
Tests metric-driven pipeline hygiene versus retry band-aids. Strong answers baseline flakiness rates, identify offenders via CI history, quarantine chronic flakes from presubmit, and fix root causes like concurrency.
Smoke test fails after canary deployment. Design the automated rollback.
Tests self-healing pipeline design: freeze canary traffic, auto-redeploy the last good release, verify rollback health, and keep failed pods for forensics. Red flag: requiring manual approval or in-place fixes instead of an atomic rollout swap.
Compare git submodules and git subtree for CI/CD
Tests dependency integration trade-offs in CI. Submodules need recursive clones and pinned commits, complicating checkout; subtree inlines code, simplifying clone but bloating history. Red flag: omitting submodule detached HEAD pain or calling subtree free.
How do you fully remove leaked credentials from Git history?
This tests Git history rewriting and incident response. Rotate the secret first, then use git-filter-repo to purge the file, force-push main, and require all teammates to re-clone before resuming. A red flag is recommending git revert or skipping rotation.
How does your CI/CD strategy differ between monoliths and microservices?
Contrast monolith unified builds with microservice independent deploys, side-by-side versions, and service gates.
Pipeline is green but lead time grows. Three areas to investigate?
This tests distinguishing pipeline health from delivery flow efficiency. A strong answer targets pre-merge wait states, slow green pipeline stages, and post-merge deployment friction, using time-in-stage metrics.
Score: Define Your Workload Once, Run Anywhere
Score is a universal remote for your workload configs, letting you define what your app needs once in a score.yaml file. It translates this spec into files for Docker Compose or Kubernetes, preventing config drift.
Crossplane: The Kubernetes Control Plane for Infrastructure
Crossplane turns your Kubernetes cluster into a universal control plane for all your cloud infrastructure, not just containers. Use it to let developers provision cloud resources like databases using familiar kubectl commands.
We are hiring for this. Every open role lists the topics its interview covers, so you can prepare for the real thing rather than guessing.
See open roles