Advanced everything in CI/CD & Automation
Critical vm2 sandbox escape (CVSS 10.0) traced to its own README example
GitLab's Threat Research Group found a CVSS 3.1: 10.0 sandbox escape in vm2, a widely used Node.js sandbox library, in a config copied from vm2's own README. Version 3.11.7 fixes the attack, but the underlying risk remains for anyone using require.external. Update immediately and prefer containers for untrusted code.
Dynamically generate CI/CD pipelines
A detection step scans for marker files and maps them to reusable stage templates assembled at runtime; trade off convention/DRY against reduced transparency and harder debugging.
How would you modify CI/CD to generate and sign SLSA provenance?
Tests SLSA Build Track L1-L3 architecture. Outline: emit in-toto provenance with builder ID and resolved deps from ephemeral runners; sign via DSSE with Sigstore; publish attestations to registry. Red flag: confusing SBOMs or image signatures with provenance.
Compare Terraform and Ansible: when to use each and both together
This tests whether you distinguish provisioning from config management. Strong answers define Terraform for immutable infra and Ansible for mutable state, contrast day 0 versus day 1-2 work, and cover Terraform for VMs and Ansible for setup.
How can artifact management and CI identify affected services and block deployments?
Tests supply chain forensics and CI gating. Strong answers hit: SBOMs mapping transitive blast radius; artifact metadata tracing deployed versions; scan gates and quarantine policies blocking promotion.
How would you integrate artifact signing into CI/CD and secure the keys?
Tests supply chain architecture and secrets management. A strong answer: remote HSM or KMS signing isolated from build runners, signature verification at deploy gates, and key rotation with audit logging.
Explain blue-green deployment, its prerequisites, and how it reduces deployment risk.
Tests operational maturity for zero-downtime cutover. Great answers: parallel environments, load balancer switching, backward-compatible schemas, externalized state, and instant rollback vs partial in-place failure.
GitLab Flex merges seats and AI into one budget
GitLab Flex reshapes one annual budget monthly across seats, AI credits, and features without re-procurement. Engineering leaders can shift spend from idle seats to agent usage instead of guessing headcount six months out. Ask at renewal.
GitLab Orbit unifies code lifecycle in live graph
GitLab Orbit beta unifies code, pipelines, and ownership in a live graph. Compare the Market tests show Orbit-grounded reviewers hit 70% accuracy versus 58% for RAG.
GitLab patches 13 CVEs including SAML account takeover flaw
GitLab 19.0.2, 18.11.5, and 18.10.8 patch 13 security flaws, including four High-severity CVEs like SAML account takeover (CVSS 8.7) and unauthenticated API DoS. Self-managed instances must upgrade immediately; GitLab.com is already patched.
How would you architect deployment capabilities for multiple disparate environments?
This tests platform design for secure multi-environment orchestration. A strong answer proposes a declarative control plane, environment-local agents with short-lived credentials, and templating for consistency.

Design a secure multi-tenant CI/CD runner on Kubernetes
Apply namespaces, NetworkPolicies, Pod Security Standards; cap resources with ResourceQuotas and LimitRanges; schedule to dedicated or sandboxed nodes.
How do you architect self-service GitOps with central policy enforcement?
What it tests: balancing self-service GitOps with hard guardrails. A strong answer covers namespace-scoped controllers, OPA/Kyverno deny policies, and a centralized policy repo. Red flag: proposing manual ticket reviews instead of automated admission gates.
How would you use GitOps to manage Kubernetes cluster lifecycles?
This tests cluster lifecycle GitOps, not just app delivery. A strong answer uses Flux plus Cluster API on a hub cluster, stores cluster definitions in Git, and rolls upgrades via MachineDeployments.
Describe a robust strategy for GitOps database schema migrations
Tests imperative-to-declarative schema reconciliation. Strong answers version idempotent pre-sync jobs and colocate schema state in Git. They use dedicated operators, not infra tools, for live execution.

How do you unify real-time CI/CD health across hundreds of microservices?
Canonical event schema over an event bus; domain-level SLI views; federated ownership with golden paths.
What statistical methods automate canary-baseline comparison and handle noise?
Tests statistical rigor in automated canary analysis. Strong answers use non-parametric tests, multi-metric aggregation with effect-size gates, MAD-based outlier rejection, and smoothing windows.
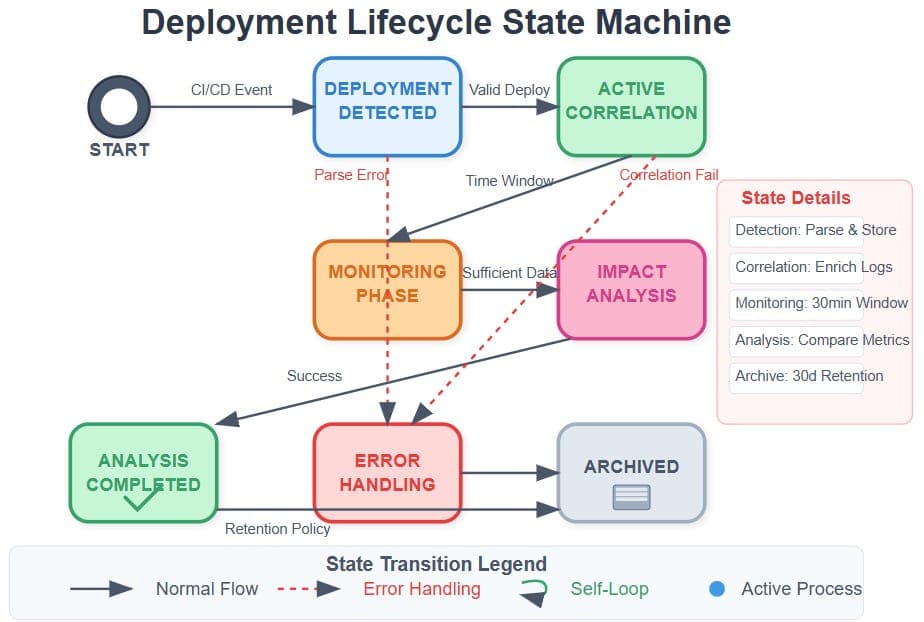
Design a system correlating CI/CD deployments with observability metrics
Tests event-driven correlation and temporal join patterns across distributed data. Strong answers outline: async deploy event ingestion, time-windowed metric joins with version tags, and handling clock skew.
How would you use a Kubernetes Admission Controller as CI/CD security gate?
Tests pre-deployment enforcement via admission webhooks. Strong answers: ValidatingAdmissionWebhooks blocking bad manifests, Pod Security Standards restricted profiles, and OPA/Gatekeeper for image signatures. Red flag: confusing with RBAC or runtime scanning.

How do you deploy a hotfix during a multi-stage canary release?
Dark-launch the fix to the canary cohort, preserve metrics, then jointly promote.
We are hiring for this. Every open role lists the topics its interview covers, so you can prepare for the real thing rather than guessing.
See open roles