Intermediate everything in DevOps & Cloud, page 15
How would you automate canary deployment and what metrics decide rollback?
This tests progressive delivery maturity. Strong answers cover traffic splitting (10% to 100%), automated 5-10 minute health gates, and rollback triggers like error rate and p99 latency.
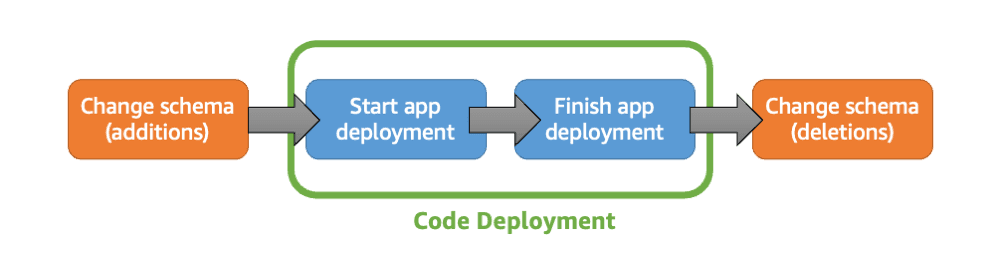
What are the major challenges of blue/green deployments with relational databases?
Tests decoupling schema and code changes in stateful blue/green deployments. Strong answers cover the additive-then-deletive pattern, backward compatibility for both app versions, and shared DB risks. Red flag: split DBs with no rollback or sync plan.

Explain the concept of a sidecar container in Kubernetes
Tests Pod multi-container patterns. A strong answer defines sidecars as co-located helpers sharing network and storage, cites service mesh or log forwarding, and argues for reuse and separate lifecycles. Red flag: calling it another Pod or legacy workaround.
How ensure Kubernetes pulls correct new image and why avoid :latest?
Tests immutable tagging and Kubernetes image pull behavior. Strong answers demand unique tags like git SHA, explicit deployment spec updates, and explain :latest's reproducibility failures across nodes.
What are liveness and readiness probes, and what happens when each fails?
This tests whether you know the distinct kubelet actions for each probe failure. A strong answer: liveness failure restarts the container; readiness failure removes the Pod from Service endpoints and stops traffic.
Compare GitOps and Kustomize vs Ansible for environment configs
Tests declarative vs imperative trade-offs. Contrast GitOps drift detection with Ansible's imperative flexibility. Note Kustomize overlays for K8s vs Ansible's broader reach.
How does your app authenticate with secrets management and solve secret zero?
This tests platform trust chains and the bootstrap credential problem. A strong answer names IAM, Kubernetes, or AppRole auth, explains platform attestation, and uses short-lived tokens.
Describe secure secret injection into Kubernetes containers during CI/CD
Tests production secret injection hygiene in Kubernetes CI/CD. Strong answers: external secret store at deploy time, volume mounts over env vars, etcd encryption, RBAC least privilege, and rotation.

Define configuration drift in IaC. How do you detect and remediate it?
This tests state divergence between declared and live infrastructure. A strong answer defines drift as deviation from the IaC source of truth, proposes automated scanning for detection, and recommends reconciliation or redeployment.
Design a CI/CD pipeline for ephemeral feature branch environments
This tests dynamic infrastructure lifecycle modeling in CI/CD. A strong answer covers branch-triggered provisioning, dynamic naming, automatic cleanup via stop jobs, and cost controls. Red flag: proposing manual teardown or static environments per branch.
Explain Terraform state, why managing it is critical, and team best practices
Tests if you know state maps config to real resources and tracks metadata. Strong answers cover remote backends with locking and encryption, never Git. Red flag: local state or ignoring that state files contain secrets.
How do you manage secrets within IaC configurations?
This tests secret injection and the security-complexity tradeoff in IaC. A strong answer contrasts a cloud secret manager with encrypted files or env vars, covering rotation and blast radius. A red flag is plaintext secrets in Git or state files.
Implement a manual approval gate for production deployment in pipeline-as-code
This tests embedding human governance in automated pipelines with auditability. A strong answer covers environment-scoped approvals, timeouts, RBAC, and immutable logs. Red flag: Ad-hoc manual deploys outside the pipeline or missing rollback plans.
How would you use PaC to introduce pipeline parallelism?
Tests splitting a sequential Jenkinsfile into independent Declarative parallel stages. Group tests and scans in a parallel block with stage-level agents, use matrix for cross-axis work, and version the Jenkinsfile.
How would you implement conditional logic in a pipeline?
Use if conditions with contexts like github.ref, separate trigger filters from runtime conditions, and add env rules.
How would you reuse pipeline steps across projects using PaC principles?
Tests DRY abstractions and coupling in CI/CD. Good answer: versioned reusable templates or libraries with parameterized inputs, consumed by composition. Red flag: raw copy-paste or one global pipeline forcing lockstep deployments.
Promote an artifact from staging to release without rebuilding it
Tests immutable artifact discipline. Answer: promote by copying the binary or retagging the image digest, never recompiling, because rebuilds introduce dependency drift and untested bits.
Explain proxy repositories in artifact managers and the problems they solve
Tests caching and supply-chain resilience in builds. Strong answers cover: local caching of upstream artifacts, shielding CI from external outages, and policy enforcement at the edge.
How do you version Docker images: Git SHA or SemVer?
Your grasp of immutable artifacts and traceability versus human-readable releases. Tag every build with Git SHA for immutability, then apply SemVer aliases only on promoted images. Treating floating tags like latest or v1 as safe production targets.
How would you integrate SAST into CI without alert fatigue?
This tests embedding security into workflow without killing velocity. Run SAST per commit, suppress false positives via rulesets, gate on high-severity findings first and block merges only after calibration. A red flag is zero-tolerance blocking on day one.
We are hiring for this. Every open role lists the topics its interview covers, so you can prepare for the real thing rather than guessing.
See open roles