Advanced concepts in CI/CD & Automation, page 2
Dynamic Pipelines: Parent-Child vs. Multi-Project
Break up monolithic CI/CD pipelines into smaller, independent ones. Use parent-child pipelines for dynamic jobs in one project (like a monorepo), or multi-project pipelines to coordinate across repos. The footgun: the parent pipeline doesn't wait by default.
Policy as Code in CI/CD with OPA
Treat pipeline rules as code using Open Policy Agent (OPA) to automate guardrails. Instead of scripts, write declarative policies to check test coverage or validate dependency licenses.

Pulumi: Infrastructure as Code with Real Programming Languages
Pulumi is Infrastructure as Code using real languages like Python or TypeScript, not a special DSL. This lets you use loops, functions, and classes to define resources. The main footgun is writing overly complex, clever code that becomes unmaintainable.
Terragrunt: A Thin Wrapper for DRY Terraform
Terragrunt is a thin wrapper for Terraform/OpenTofu that automates common tasks. Just add an empty terragrunt.hcl file to get features like automatic init.
Open Policy Agent (OPA): Centralized Policy as Code
OPA decouples policy decisions from your app's code. Instead of scattering if statements, you query a central engine: 'Is this allowed?' It enforces rules in Kubernetes, CI/CD, and API gateways. A common footgun is only using it for yes/no decisions.
Cloud-Init: Bootstrapping Cloud Instances
Cloud-init is the script that runs on a generic VM's first boot to turn it into *your* server. It's used by cloud providers to apply your user-data (like SSH keys and startup scripts) at launch. The biggest footgun: it only runs once on first boot.
Kubernetes Sealed Secrets: Git-Friendly Secret Management
Sealed Secrets let you safely commit encrypted Kubernetes secrets to a public Git repo. A one-way lockbox: anyone can add a secret, but only the target cluster can unlock it. Essential for GitOps, but remember: a Sealed Secret is tied to its cluster.
External Secrets Operator: Sync Secrets into Kubernetes
The External Secrets Operator (ESO) acts as a bridge, syncing secrets from an external store like Vault or AWS Secrets Manager into native Kubernetes Secrets. This keeps secrets out of Git and centralizes management.

Kubernetes StatefulSets: Stable Identity for Pods
A StatefulSet gives pods a stable, unique identity and persistent storage, unlike a Deployment's interchangeable replicas. Use it for clustered databases or queues where members need stable network names.
Service Mesh: The Network Layer for Your Microservices
A service mesh acts as a dedicated network layer for microservices, handling complex communication logic outside your application. It enables features like mTLS and canary releases.
CNI: The Universal Plug for Container Networking
CNI is the standard API that decouples container runtimes from network implementations. In Kubernetes, it lets you swap networking plugins like Calico or Flannel.
Kubernetes Operators: SREs in a Box
Think of an Operator as an automated site reliability engineer for your app, encoding human knowledge into software. It's used to manage complex stateful applications like databases, automating tasks like backups and upgrades.
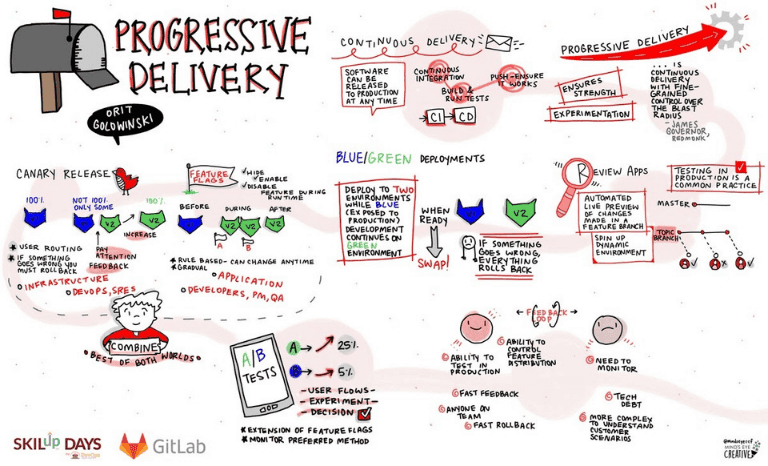
Progressive Delivery: Ship Faster by Reducing Blast Radius
Progressive Delivery reduces release risk by shipping to small user groups before a full rollout, like a soft-opening for new code. It uses canary releases and feature flags to catch issues before they impact everyone.
Release Orchestration: Air Traffic Control for Deployments
Release Orchestration is the air traffic control for software delivery, coordinating multiple pipelines and teams. It's used for complex launches with interdependent services, ensuring everything deploys in the correct sequence.

Environment Gating: Automated Go/No-Go for Deployments
Environment gating is an automated checklist for your CI/CD pipeline. Instead of just building code, it checks external signals like monitoring alerts or bug trackers before promoting a release.
RASP: An Immune System for Your Application
Think of RASP as an application's immune system, using runtime instrumentation to block attacks from within. It provides real-time protection against threats that static analysis or network firewalls miss.
CI/CD and the Principle of Least Privilege
Treat your CI/CD pipeline like a temporary worker, not a superuser. Grant it only the minimum permissions needed for its specific task, like building code or deploying to staging.
Analyzing Flaky Tests
A flaky test passes and fails randomly without code changes, eroding trust in your CI pipeline. It often points to race conditions or external dependencies. The biggest footgun is ignoring them, as this teaches developers to dismiss real failures.
Chaos Engineering: Break Systems to Build Confidence
Chaos Engineering is like a fire drill for your software: you intentionally break things in a controlled way to find weaknesses. It's used in distributed systems to test resilience against server failures or network latency.
eBPF: Run Sandboxed Programs in the Linux Kernel
eBPF lets you run sandboxed programs directly in the Linux kernel, like adding programmable event handlers to your OS. This enables high-performance networking, security, and observability without changing kernel code.
We are hiring for this. Every open role lists the topics its interview covers, so you can prepare for the real thing rather than guessing.
See open roles