Concepts in CI/CD & Automation, page 2
Git Cherry-Pick: Copy a Commit to Another Branch
Think of git cherry-pick as copying a single commit's changes from one branch and reapplying them as a new commit on another. It's for backporting a bug fix without merging an entire feature branch.
Monorepo vs. Polyrepo: One Repository or Many?
A monorepo is one repository for all projects, like a city; a polyrepo is one per project, like separate towns. Monorepos simplify code sharing and atomic refactors but require complex tooling. Polyrepos offer autonomy but can create dependency hell.
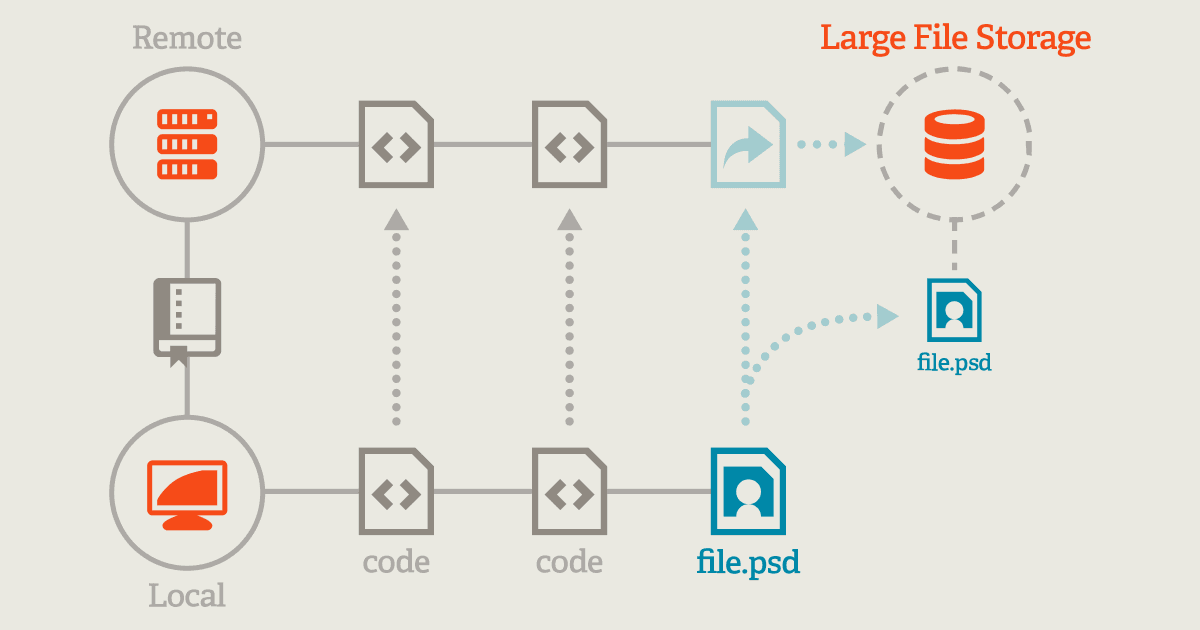
Git LFS: Versioning Large Files Without Bloating Your Repo
Git LFS replaces large files with text pointers in your repo, storing the actual data on a remote server. This keeps clones fast when versioning videos, datasets, or graphics. Footgun: git lfs track only affects new files, not existing ones.

Build Artifact: The Packaged Output of a CI Run
A build artifact is the packaged result of a CI run, like a compiled binary or a zipped web app. Pipelines use artifacts to pass this output between stages, from building to testing and deploying.
Make: The Original Task Runner
Make automates tasks by following a recipe in a makefile. It intelligently runs only the necessary steps by checking dependencies, saving time during builds. While common for compiling code, it can run any shell command.
Build Dependency Management: Your Project's Recipe
Dependency management is your project's recipe, ensuring everyone uses the same library versions. It's used everywhere from web apps pulling React via npm to Java services using Maven.
Static Analysis: Read Code, Don't Run It
Static analysis is like a spell checker for your code, catching errors before you run the program. It powers linters and security scanners in CI pipelines to find bugs and vulnerabilities. The footgun: it can't understand intent, leading to false positives.
Apache Maven: Convention Over Configuration for Builds
Maven standardizes your build process using a 'convention over configuration' model, defining project structure and dependencies declaratively. It's the backbone of many Java projects, ensuring consistent builds. The footgun is fighting its conventions.
Gradle: Code-Based Builds, Not XML
Gradle treats your build process like code, not configuration, using a flexible Groovy or Kotlin DSL instead of rigid XML. It's used for compiling and packaging multi-language projects.
Maven's Build Lifecycle: A Sequence of Build Phases
Maven's build lifecycle is a predefined sequence of phases like compile, test, and package. Running a phase executes all preceding ones, ensuring a consistent build.
Code Coverage: What Your Tests Don't Tell You
Code coverage measures which lines of code your tests execute, not how well they're tested. It's used in CI to enforce a testing baseline, but the footgun is mistaking high coverage for high quality—100% coverage can exist with zero useful assertions.
Incremental Build: Develop and Ship Software in Pieces
Incremental builds deliver software in usable chunks, not one big release. This lets you ship value and gather feedback early on large projects. The footgun is poor planning, leading to disconnected features and architectural debt instead of a cohesive…
Reproducible Builds: Trust What You Run
A reproducible build guarantees that the same source code always compiles into the exact same binary. This is crucial for verifying that a distributed application wasn't tampered with.
Cross-Compilation: Build Anywhere, Run Elsewhere
A cross-compiler builds code for a different machine than the one it runs on. This lets you use a powerful PC to compile for a tiny IoT device or a mobile phone. The footgun is forgetting that the target's OS and libraries matter, not just.
Build Matrix: Test All The Combinations
A build matrix automatically creates multiple jobs by combining different configurations. Use it to test your code across various operating systems, language versions, or dependencies without duplicating your workflow file.
Unit Testing: Verifying Code's Smallest Parts
Think of unit tests as checking each Lego brick for defects before building the castle. They confirm your smallest code pieces, like a single function, behave correctly in isolation.
Integration Testing: Do Your Components Play Well Together?
Integration testing verifies that different software modules, like an API and a database, work correctly together. It's used to catch bugs in the interactions between components, such as data format mismatches. The footgun is writing slow, brittle tests.
Smoke Testing: Is This Build Even Worth Testing?
Smoke testing asks: 'Is this build so broken it's not even worth testing?' It's a quick, shallow check of critical functions, run on every new build before more exhaustive QA. The footgun is thinking a passed smoke test means the build is bug-free.
Quality Gates: Your Automated Code Quality Checklist
A quality gate is an automated checklist that asks, 'Is this code ready to release?' It runs in CI/CD to enforce standards on metrics like bugs and test coverage, blocking merges that fail. The footgun is using one gate for all projects; tailor rules to.
Regression Testing: Don't Break What's Already Working
Regression testing asks: 'Did my new code break old features?' It's re-running existing tests after a change to catch unintended side effects. It's crucial in CI/CD pipelines before deploying. The footgun is a slow suite that developers skip.
We are hiring for this. Every open role lists the topics its interview covers, so you can prepare for the real thing rather than guessing.
See open roles