Intermediate everything in DevOps & Cloud, page 27
Flux CD: Git as the Source of Truth for Kubernetes
Flux CD makes Git your cluster's source of truth. It automatically syncs Kubernetes manifests from a repo to your cluster, ensuring the live state matches your config. This is for continuous delivery, not CI.
Pipeline Analytics: Measuring Your CI/CD Health
Pipeline analytics is a fitness tracker for your CI/CD, revealing if builds are getting slower or less reliable. Use it to spot bottlenecks, track failure rates, and compare branches. The footgun is ignoring the P95 duration, which hides worst-case outliers.

DORA Metrics: Vital Signs for Your CI/CD Pipeline
DORA metrics are four vital signs for your software delivery process, balancing speed and stability. They benchmark DevOps performance from commit to production. The main footgun is optimizing for speed while ignoring stability, leading to frequent outages.
Synthetic Monitoring: Probing Your App Like a Robot User
Synthetic monitoring is like having a robot user click through your app's critical paths 24/7 to catch issues before real users do. It tests key flows like login or checkout, providing a consistent baseline for performance.
Real User Monitoring (RUM): See Your App Through Users' Eyes
Real User Monitoring (RUM) is like a flight recorder for your app, capturing real user clicks, load times, and errors. It's used to measure actual performance and diagnose slowdowns, revealing issues that lab testing misses.
Service Level Objective (SLO): A Measurable Promise
An SLO is a precise, measurable promise about your service's performance, like "99.9% of requests will succeed." It's the internal engineering target that backs up a customer-facing SLA. The footgun is setting a 100% SLO, which leaves no room for failure.
Distributed Tracing: Following a Request Across Microservices
Distributed tracing is like a passport for a request, stamped at every service it visits. It's essential for debugging microservices where one click can trigger many calls. The footgun is trying to debug without it, piecing together isolated logs.
The Vulnerability Management Lifecycle: A Continuous Loop
Think of vulnerability management not as a one-off task, but a continuous cycle of finding, prioritizing, fixing, and verifying security weaknesses. This process is crucial for securing any system by systematically reducing its attack surface.
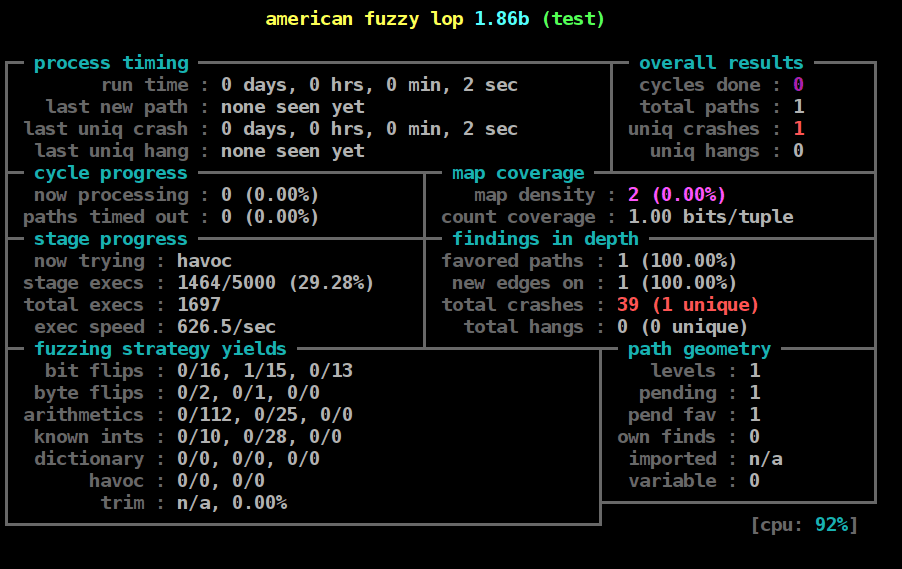
Fuzz Testing: Finding Bugs with Random, Invalid Inputs
Fuzz testing is automated chaos engineering for your inputs. It feeds your program semi-random, invalid data to uncover crashes and security flaws, especially in code that parses files or network protocols.
Deployment Rings: De-risking Rollouts with Progressive Exposure
Deployment rings are like blast shields for software updates, containing a bad release's impact to a small group. They're used in CI/CD to roll out changes progressively, from internal teams to all users.
Shadow Deployment: Rehearsing a Release with Live Traffic
Shadow deployment is like a stunt double for your service: it receives a copy of live production traffic to test a new version without impacting users. Use it to validate performance and find bugs under real load.
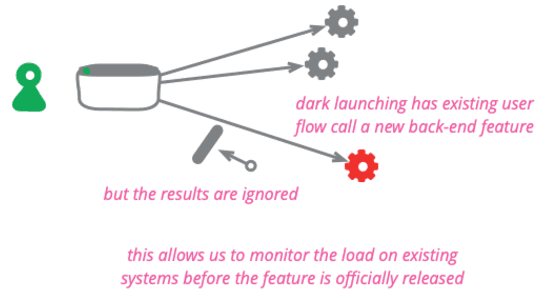
Dark Launch: Test New Code Invisibly in Production
A dark launch tests new backend code on real production traffic without any user ever seeing it. Use it to measure the performance impact of a new recommendation engine or data service before the UI is built.
Traffic Shaping for Safer Deployments
In deployments, traffic shaping isn't about network speed, but controlling user exposure. You route a precise percentage of users to a new code version, slowly 'opening the valve' from 1% to 100% to de-risk the release. This is the engine of a canary deploy.

Kubernetes Health Checks: Liveness, Readiness, and Startup Probes
Kubernetes health checks ask your app: "Are you alive?" (liveness), "Ready for traffic?" (readiness), and "Done starting?" (startup). This lets it automate restarts and traffic routing for zero-downtime deployments.
Kubernetes Ingress: The Cluster's Front Door
Kubernetes Ingress is the smart receptionist for your cluster. It routes external HTTP/S requests to internal services based on hostnames or paths, letting you expose multiple apps under one IP.
Helm: The Package Manager for Kubernetes
Helm is the package manager for Kubernetes. It uses a packaging format called Charts to define, install, and upgrade applications, making it the standard way to manage software on a K8s cluster. It is a Cloud Native Computing Foundation (CNCF) project.
Kubernetes Service: A Stable Address for Ephemeral Pods
A Kubernetes Service provides a stable IP address and DNS name for a group of ephemeral Pods. It acts like a load balancer, distributing traffic so you don't have to track individual Pod IPs, which can change at any time.
Kubernetes Deployment: Declarative App Updates
A Kubernetes Deployment is your app's blueprint. You declare the desired state—like '3 replicas of image v2'—and Kubernetes makes it happen. It's the standard for stateless apps like APIs. The footgun: don't manage Pods directly; manage the Deployment.
Kubernetes Pods: The Atomic Unit of Deployment
A Kubernetes Pod is the atomic unit of deployment, a logical host for containers sharing a network and storage. This is ideal for co-locating a main app with a helper "sidecar" container. The footgun: a Pod is not a container; you scale by adding more.
Kubernetes: The Operating System for Your Cluster
Think of Kubernetes as an OS for your entire datacenter. It automates deploying, scaling, and managing containerized applications across a fleet of servers. The footgun is adopting it for simple projects, where its complexity outweighs its benefits.
We are hiring for this. Every open role lists the topics its interview covers, so you can prepare for the real thing rather than guessing.
See open roles