Advanced everything in CI/CD & Automation, page 4
Open Policy Agent (OPA): Centralized Policy as Code
OPA decouples policy decisions from your app's code. Instead of scattering if statements, you query a central engine: 'Is this allowed?' It enforces rules in Kubernetes, CI/CD, and API gateways. A common footgun is only using it for yes/no decisions.
Terragrunt: A Thin Wrapper for DRY Terraform
Terragrunt is a thin wrapper for Terraform/OpenTofu that automates common tasks. Just add an empty terragrunt.hcl file to get features like automatic init.

Pulumi: Infrastructure as Code with Real Programming Languages
Pulumi is Infrastructure as Code using real languages like Python or TypeScript, not a special DSL. This lets you use loops, functions, and classes to define resources. The main footgun is writing overly complex, clever code that becomes unmaintainable.
Policy as Code in CI/CD with OPA
Treat pipeline rules as code using Open Policy Agent (OPA) to automate guardrails. Instead of scripts, write declarative policies to check test coverage or validate dependency licenses.
Dynamic Pipelines: Parent-Child vs. Multi-Project
Break up monolithic CI/CD pipelines into smaller, independent ones. Use parent-child pipelines for dynamic jobs in one project (like a monorepo), or multi-project pipelines to coordinate across repos. The footgun: the parent pipeline doesn't wait by default.
Pipeline Templates: Reusable CI/CD Building Blocks
Think of pipeline templates as versioned, shareable functions for your CI/CD. Instead of copy-pasting YAML, you import a standardized block of logic for tasks like security scanning or deployment.
Artifact Vulnerability Scanning: A Background Check for Code
Artifact vulnerability scanning is a background check for your software's dependencies, catching known security issues before they ship. It's a key CI/CD step, automatically scanning Docker images against databases of known CVEs. The footgun is alert fatigue.
Artifact Promotion: Build Once, Deploy Everywhere
Artifact promotion means you build software once, then deploy that exact same package to every environment. This prevents "it worked in staging" failures caused by rebuilds pulling different dependencies. The footgun is rebuilding per environment.
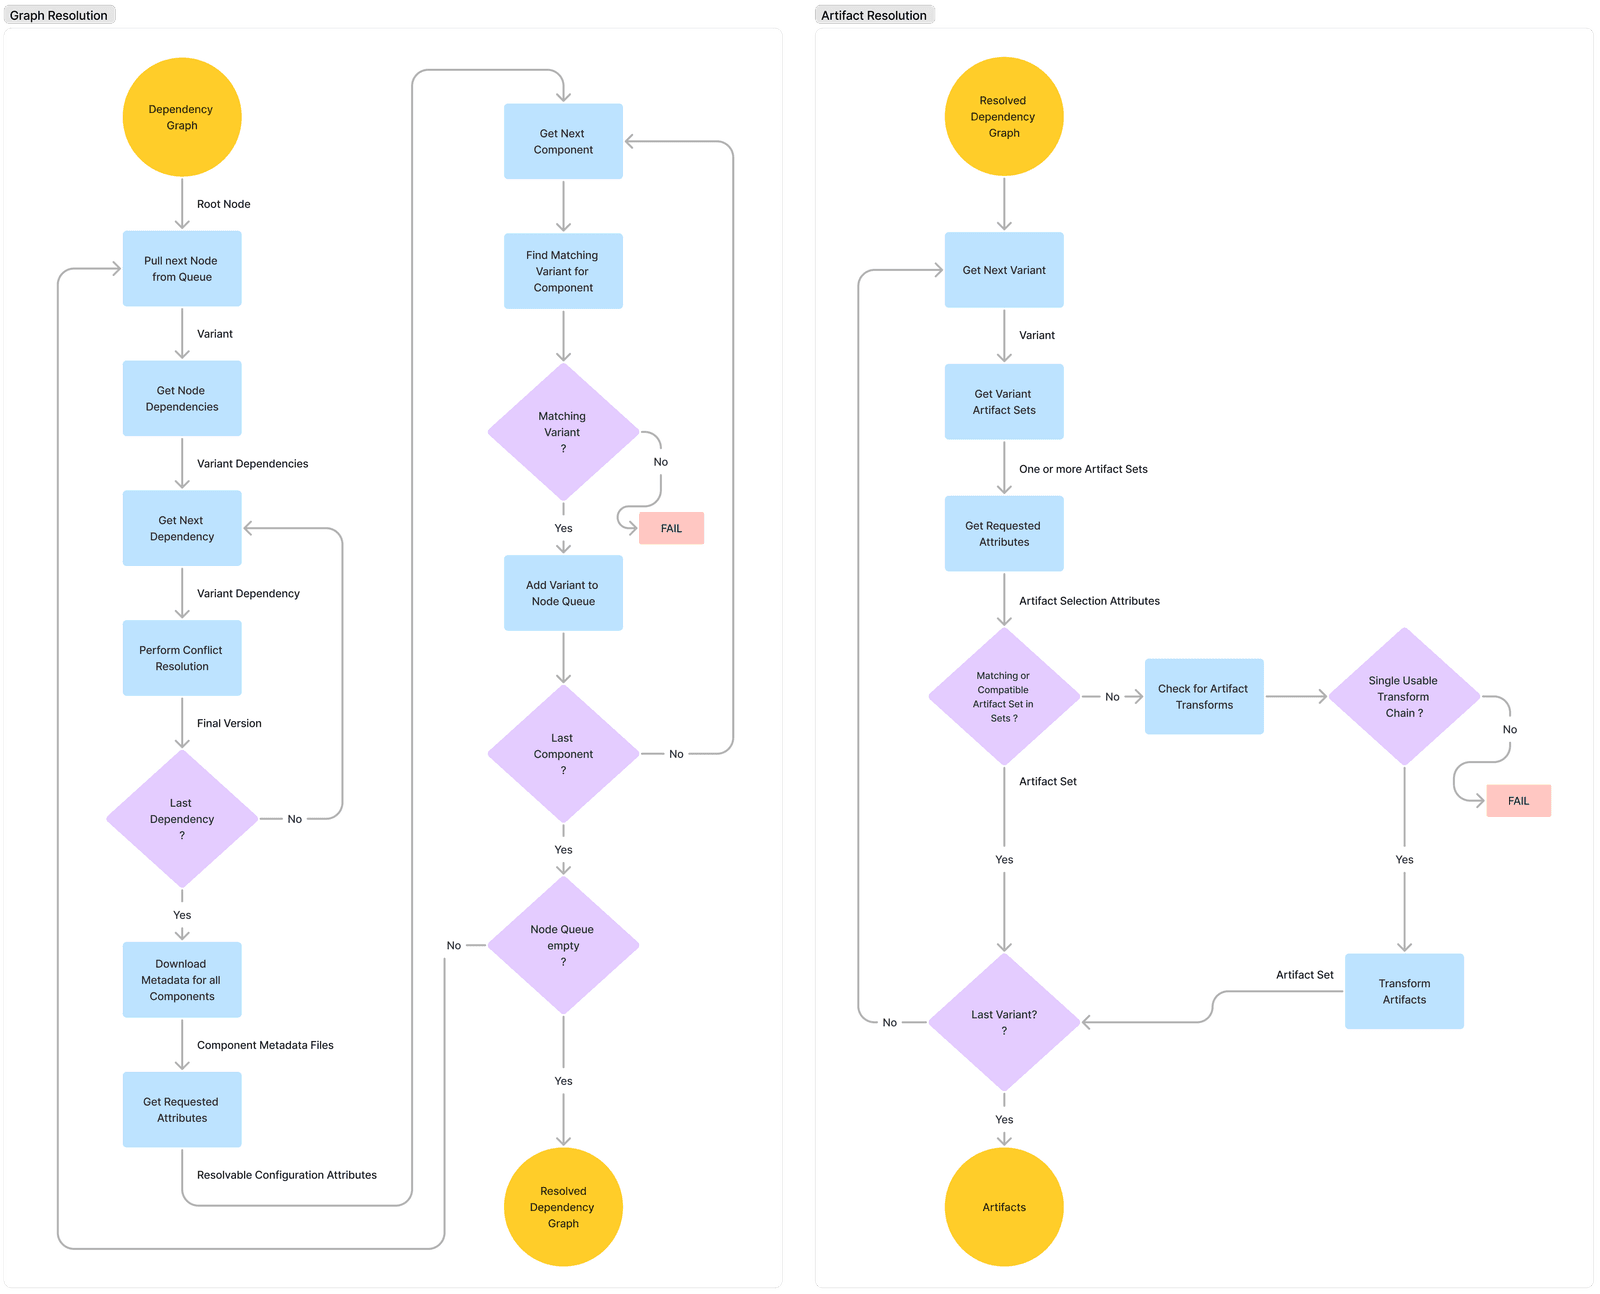
Dependency Conflict: When Your Dependencies Disagree
A dependency conflict occurs when two of your project's dependencies require different, incompatible versions of a shared library. This is common in any project with a dependency graph, forcing your build tool to pick one version, which can introduce subtle…

Software Bill of Materials (SBOM): An Ingredient List for Your Code
An SBOM is a nutrition label for your code, listing every library and dependency. It's crucial for security audits and managing supply chain risk, letting you instantly find systems affected by a new vulnerability.
Test Data Management (TDM): Stop Flaky Tests
Test Data Management (TDM) treats test data like code: versioned, managed, and reliably provisioned to ensure consistent, meaningful tests. This is crucial in CI/CD pipelines where automated tests require repeatable data states.
DAST: Probing a Running App for Security Flaws
DAST acts like an automated pen-tester, attacking your running application from the outside to find flaws without seeing the code. It's used in CI/CD to catch common web vulnerabilities. The footgun: DAST can't see the code, so it misses business logic errors.
Mutation Testing: A Fire Drill for Your Test Suite
Mutation testing is a fire drill for your test suite. It deliberately injects small bugs ('mutants') into your code to see if your tests fail as expected. This ensures tests validate behavior, not just execute lines.
Build Matrix: Test All The Combinations
A build matrix automatically creates multiple jobs by combining different configurations. Use it to test your code across various operating systems, language versions, or dependencies without duplicating your workflow file.
Cross-Compilation: Build Anywhere, Run Elsewhere
A cross-compiler builds code for a different machine than the one it runs on. This lets you use a powerful PC to compile for a tiny IoT device or a mobile phone. The footgun is forgetting that the target's OS and libraries matter, not just.
Reproducible Builds: Trust What You Run
A reproducible build guarantees that the same source code always compiles into the exact same binary. This is crucial for verifying that a distributed application wasn't tampered with.
Incremental Build: Develop and Ship Software in Pieces
Incremental builds deliver software in usable chunks, not one big release. This lets you ship value and gather feedback early on large projects. The footgun is poor planning, leading to disconnected features and architectural debt instead of a cohesive…
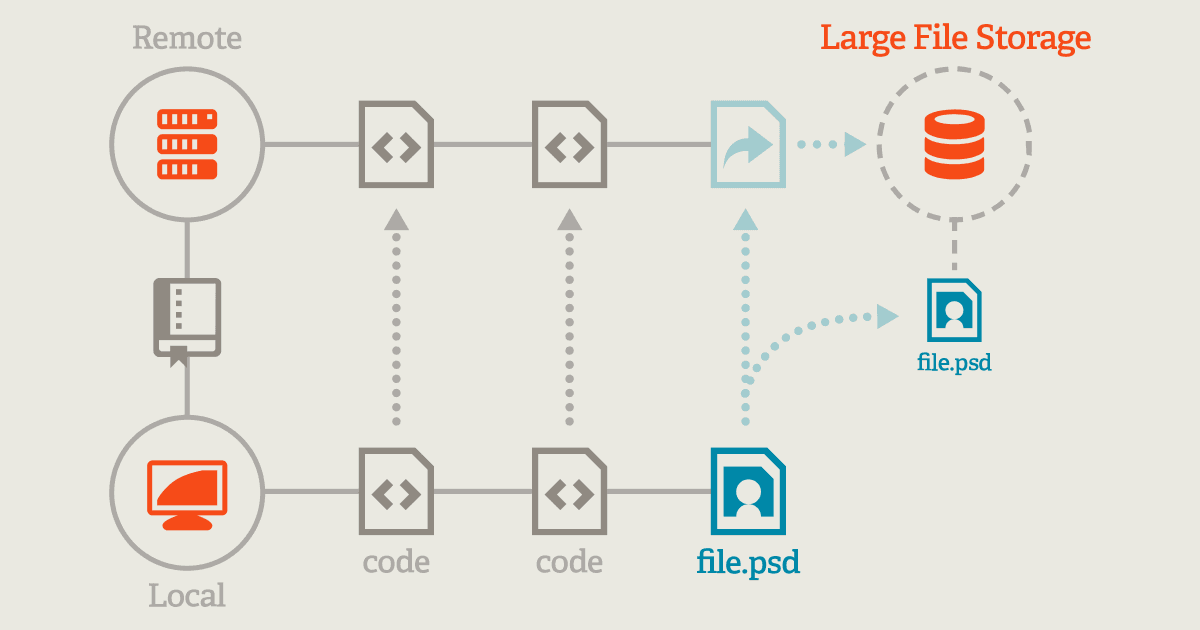
Git LFS: Versioning Large Files Without Bloating Your Repo
Git LFS replaces large files with text pointers in your repo, storing the actual data on a remote server. This keeps clones fast when versioning videos, datasets, or graphics. Footgun: git lfs track only affects new files, not existing ones.
Monorepo vs. Polyrepo: One Repository or Many?
A monorepo is one repository for all projects, like a city; a polyrepo is one per project, like separate towns. Monorepos simplify code sharing and atomic refactors but require complex tooling. Polyrepos offer autonomy but can create dependency hell.
Git Cherry-Pick: Copy a Commit to Another Branch
Think of git cherry-pick as copying a single commit's changes from one branch and reapplying them as a new commit on another. It's for backporting a bug fix without merging an entire feature branch.
We are hiring for this. Every open role lists the topics its interview covers, so you can prepare for the real thing rather than guessing.
See open roles